How to connect a domain to web hosting or a VPS without breaking email
Find the authoritative DNS zone, choose the right A, AAAA or CNAME record, prepare HTTPS and verify the cutover.
Updated
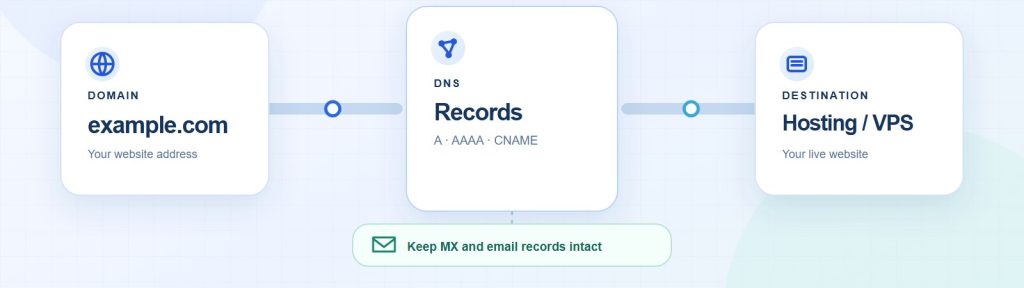
Buying a domain and connecting it to hosting are separate jobs. The registrar records ownership and delegates DNS; your authoritative DNS provider answers the records that point visitors to a web server. Decide who manages each part before changing records, especially if email is already working.
Find the authoritative DNS and current records
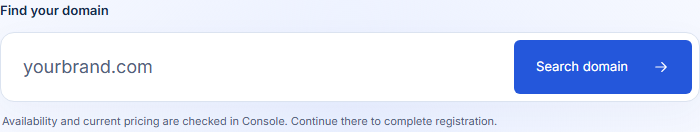
Record the domain’s nameservers, current A, AAAA, CNAME, MX and TXT records, and who can edit them. Do not delete mail or verification records just because the website is moving. A domain ordered through GhostVPS Domain can be used with hosting or a VPS, but you still need to manage its active DNS zone with the authoritative provider. The domain-search screenshot below is a real entry point; availability and final price are checked in Console.
Choose the record that matches the destination
An A record points a name to an IPv4 address; AAAA is the IPv6 equivalent. A CNAME points one name to another hostname. The authoritative DNS service may support special handling at the zone apex, so follow that provider’s instructions. Cloudflare’s record-type reference explains the fields and TTL. Use the exact server IP or hostname shown for your selected Web Hosting or Cloud VPS service; do not copy a sample address from an article.
| Goal | Typical record | Verify |
|---|---|---|
| Root website | A or AAAA at the root name | It reaches the correct web server |
| www website | CNAME to the chosen canonical hostname, where supported | It redirects or serves the intended site |
| Email delivery | Existing MX and related TXT records | Mail still arrives and authentication passes |
| Ownership verification | Provider-specific TXT or CNAME | The provider recognizes the record |
Prepare HTTPS and the cutover
Install and test the site on the destination first. Ensure its TLS certificate covers the hostname, configure the intended canonical URL, and check a few important old paths. Then update the authoritative record. Resolver caches may continue using old answers until their TTL expires; changing a record is not always instantaneous. If you use a proxying DNS provider, understand whether the hostname is proxied or DNS-only and whether the service uses HTTP/HTTPS. Cloudflare’s record setup guide documents that choice.
Verify from the user’s point of view
After the change, check DNS answers from more than one network, open both the root and www addresses over HTTPS, follow their redirects, submit a safe contact-form test and confirm mail remains intact. Keep the old server available until the change is stable. If the destination is a migrated WordPress site, follow the WordPress migration and rollback plan so the database and uploads remain consistent.
Reviewed 31 October 2026. The exact record values depend on your live service and authoritative DNS provider.